Deploy a Bun application on AWS Lambda
AWS Lambda is a serverless compute service that lets you run code without provisioning or managing servers.
This guide deploys a Bun HTTP server to AWS Lambda using a Dockerfile.
Note
Before continuing, make sure you have:
- A Bun application ready for deployment
- An AWS account
- AWS CLI installed and configured
- Docker installed and added to your
PATH
-
Create a new Dockerfile
Create a new
Dockerfilein the root of your project. This file contains the instructions to initialize the container, copy your local project files into it, install dependencies, and start the application.# Use the official AWS Lambda adapter image to handle the Lambda runtime FROM public.ecr.aws/awsguru/aws-lambda-adapter:1.0.1 AS aws-lambda-adapter # Use the official Bun image to run the application FROM oven/bun:debian AS bun_latest # Copy the Lambda adapter into the container COPY --from=aws-lambda-adapter /lambda-adapter /opt/extensions/lambda-adapter # Set the port to 8080. This is required for the AWS Lambda adapter. ENV PORT=8080 # Set the work directory to `/var/task`. This is the default work directory for Lambda. WORKDIR "/var/task" # Copy the package.json and bun.lock into the container COPY package.json bun.lock ./ # Install the dependencies RUN bun install --production --frozen-lockfile # Copy the rest of the application into the container COPY . /var/task # Run the application. CMD ["bun", "index.ts"]Note
Make sure that the start command corresponds to your application's entry point. The start command can also be
CMD ["bun", "run", "start"]if you have a start script in yourpackage.json.If your app doesn't have dependencies, you can omit the
COPY package.json bun.lock ./andRUN bun install --production --frozen-lockfilelines. Bun doesn't write abun.lockfor a project with no dependencies.Create a new
.dockerignorefile in the root of your project. It lists the files and directories to exclude from the container image, such asnode_modules. Excluding them keeps builds faster and smaller:node_modules Dockerfile* .dockerignore .git .gitignore README.md LICENSE .vscode .env # Any other files or directories you want to exclude -
Build the Docker image
Make sure you're in the directory containing your
Dockerfile, then build the Docker image. This example names the imagebun-lambda-demoand tags it aslatest.# cd /path/to/your/app docker build --provenance=false --platform linux/amd64 -t bun-lambda-demo:latest . -
Create an ECR repository
Before pushing the image, create an ECR repository to push it to.
The following command:
- Creates an ECR repository named
bun-lambda-demoin theus-east-1region - Exports the repository URI as an environment variable. The export is optional, but it makes the next steps easier.
export ECR_URI=$(aws ecr create-repository --repository-name bun-lambda-demo --region us-east-1 --query 'repository.repositoryUri' --output text) echo $ECR_URI[id].dkr.ecr.us-east-1.amazonaws.com/bun-lambda-demoNote
If you're using IAM Identity Center (SSO) or have configured AWS CLI with profiles, add the
--profileflag to your AWS CLI commands.For example, if your profile is named
my-sso-app, use--profile my-sso-app. Runaws configure list-profilesto see your available profiles.export ECR_URI=$(aws ecr create-repository --repository-name bun-lambda-demo --region us-east-1 --profile my-sso-app --query 'repository.repositoryUri' --output text) echo $ECR_URI - Creates an ECR repository named
-
Authenticate with the ECR repository
Log in to the ECR repository:
aws ecr get-login-password --region us-east-1 | docker login --username AWS --password-stdin $ECR_URILogin SucceededNote
If using a profile, use the
--profileflag:aws ecr get-login-password --region us-east-1 --profile my-sso-app | docker login --username AWS --password-stdin $ECR_URI -
Tag and push the docker image to the ECR repository
Make sure you're in the directory containing your
Dockerfile, then tag the Docker image with the ECR repository URI.docker tag bun-lambda-demo:latest ${ECR_URI}:latestThen, push the image to the ECR repository.
docker push ${ECR_URI}:latest -
Create an AWS Lambda function
Go to AWS Console > Lambda > Create Function > Select Container image
Warning
Make sure you've selected the right region. This URL defaults to
us-east-1.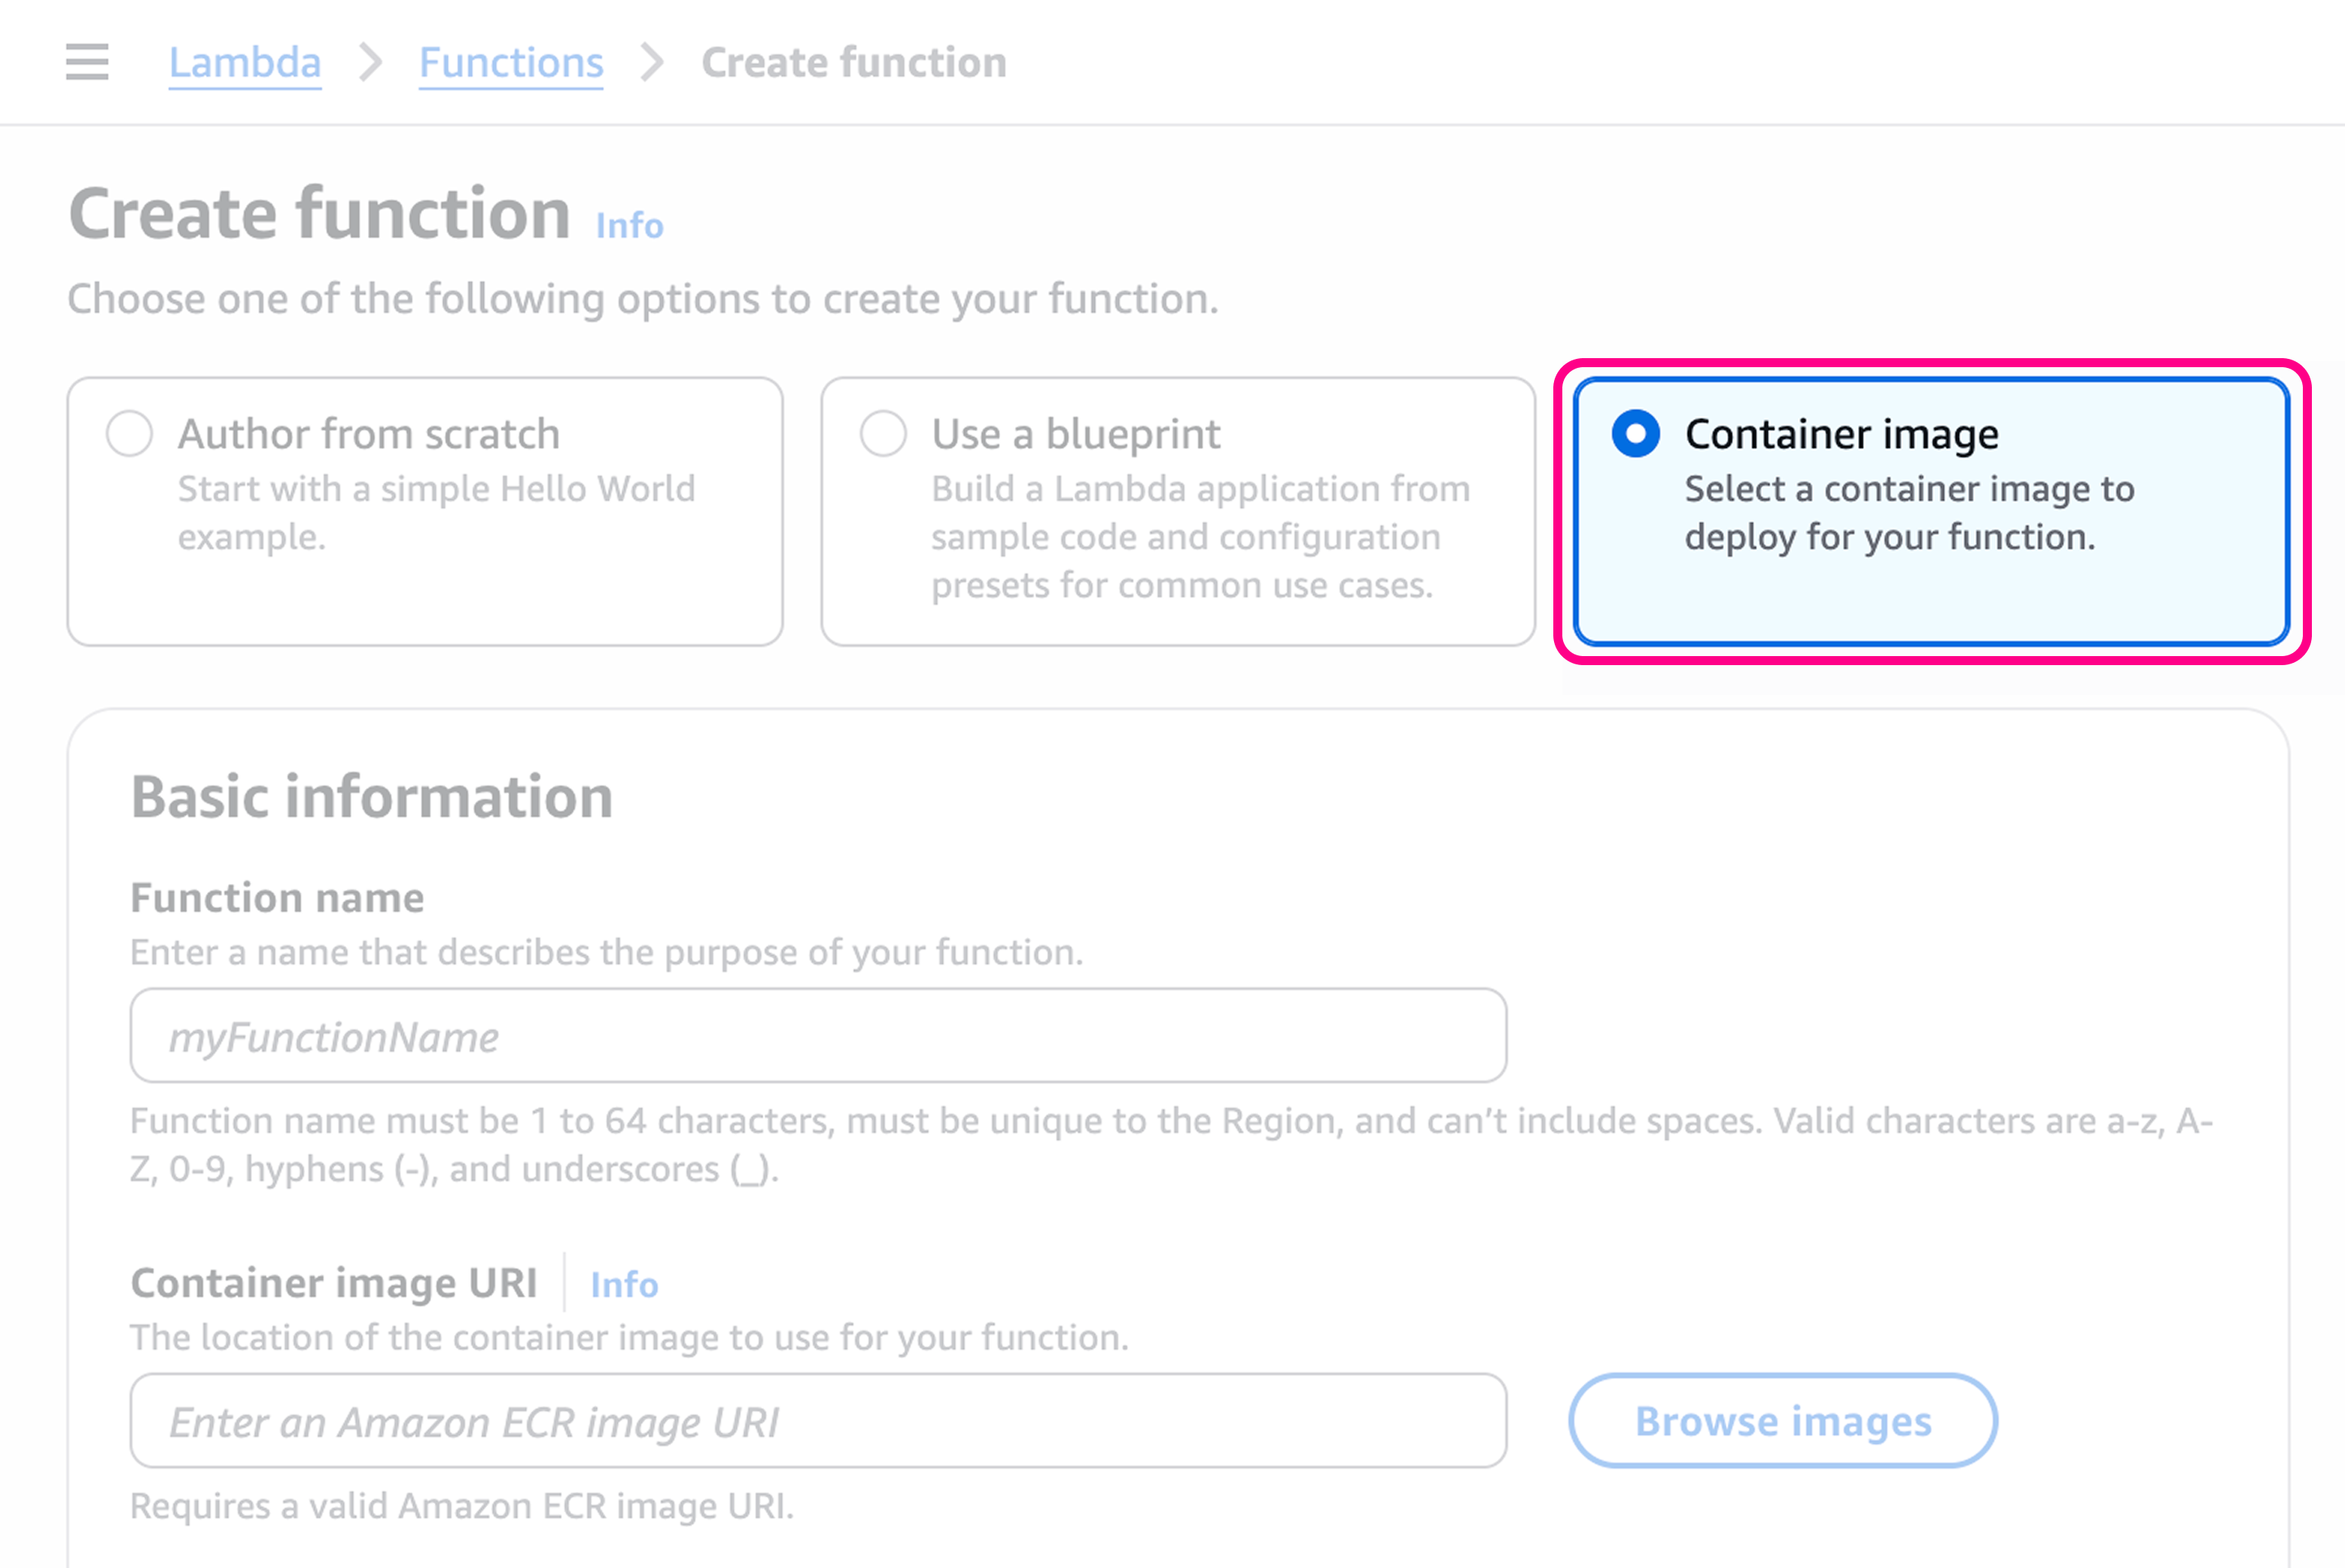
Give the function a name, like
my-bun-function. -
Select the container image
Go to the Container image URI section and click Browse images. Select the image you pushed to the ECR repository.
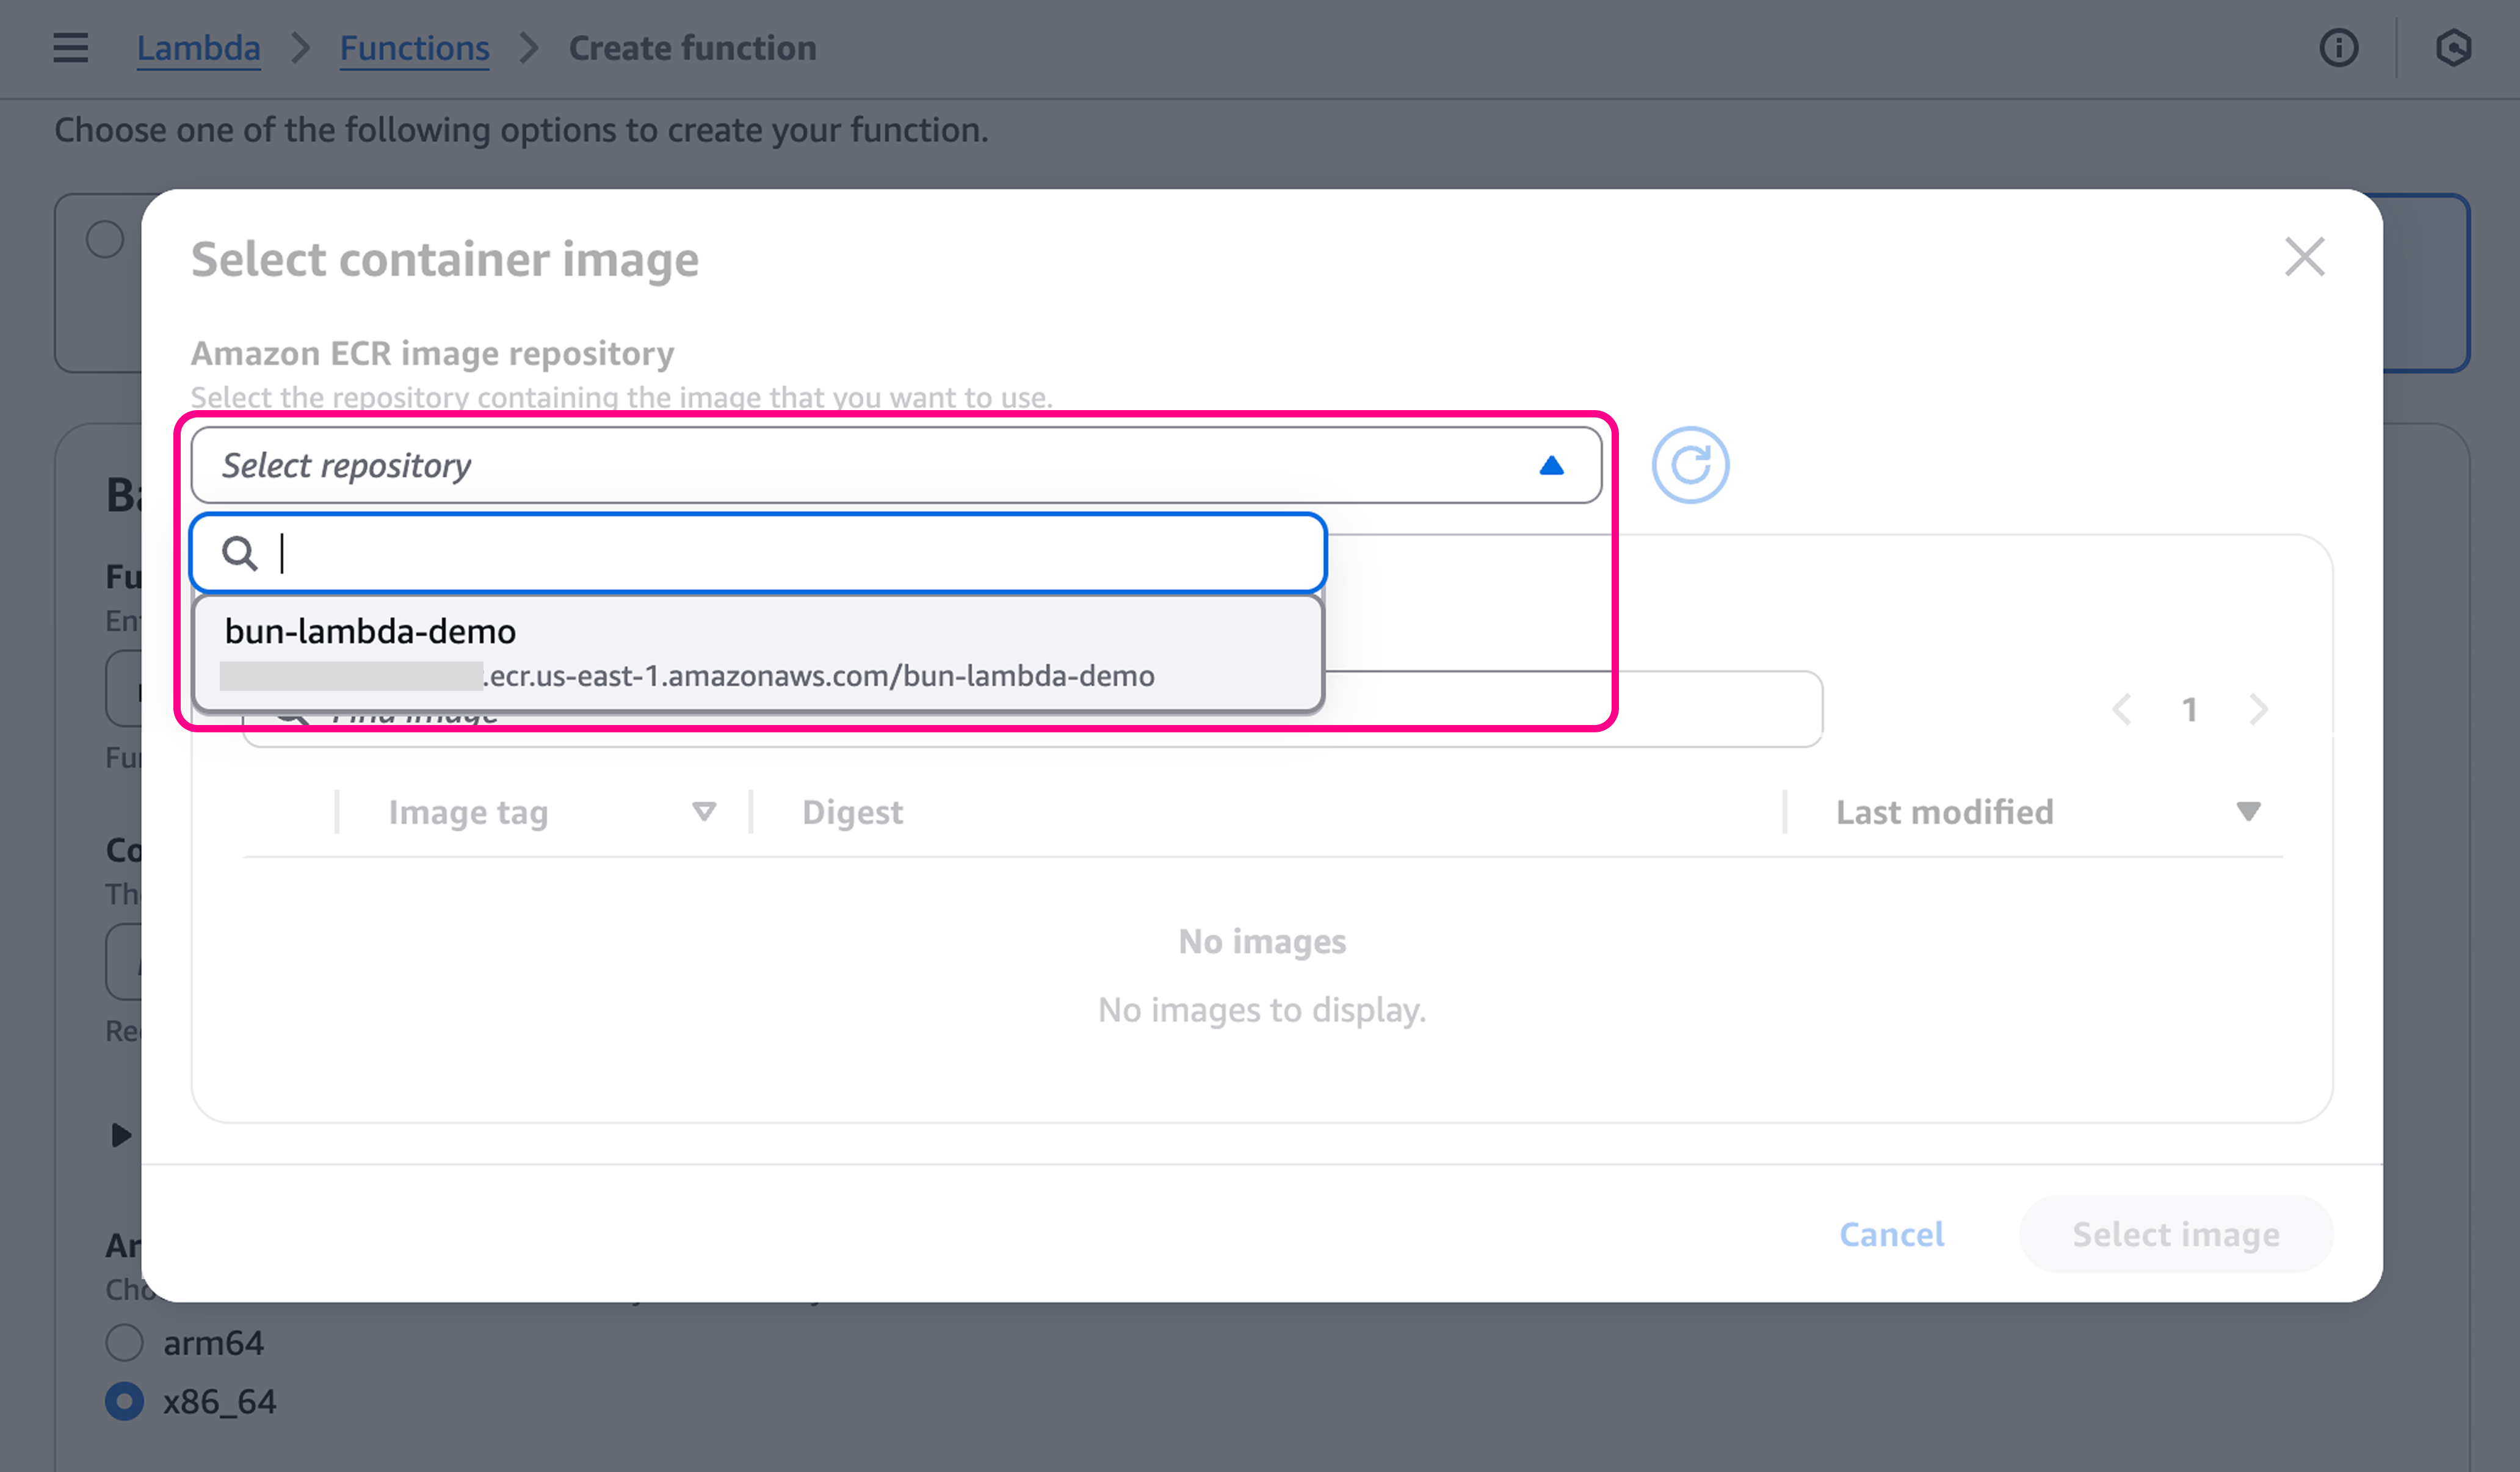
Then, select the
latestimage and click Select image.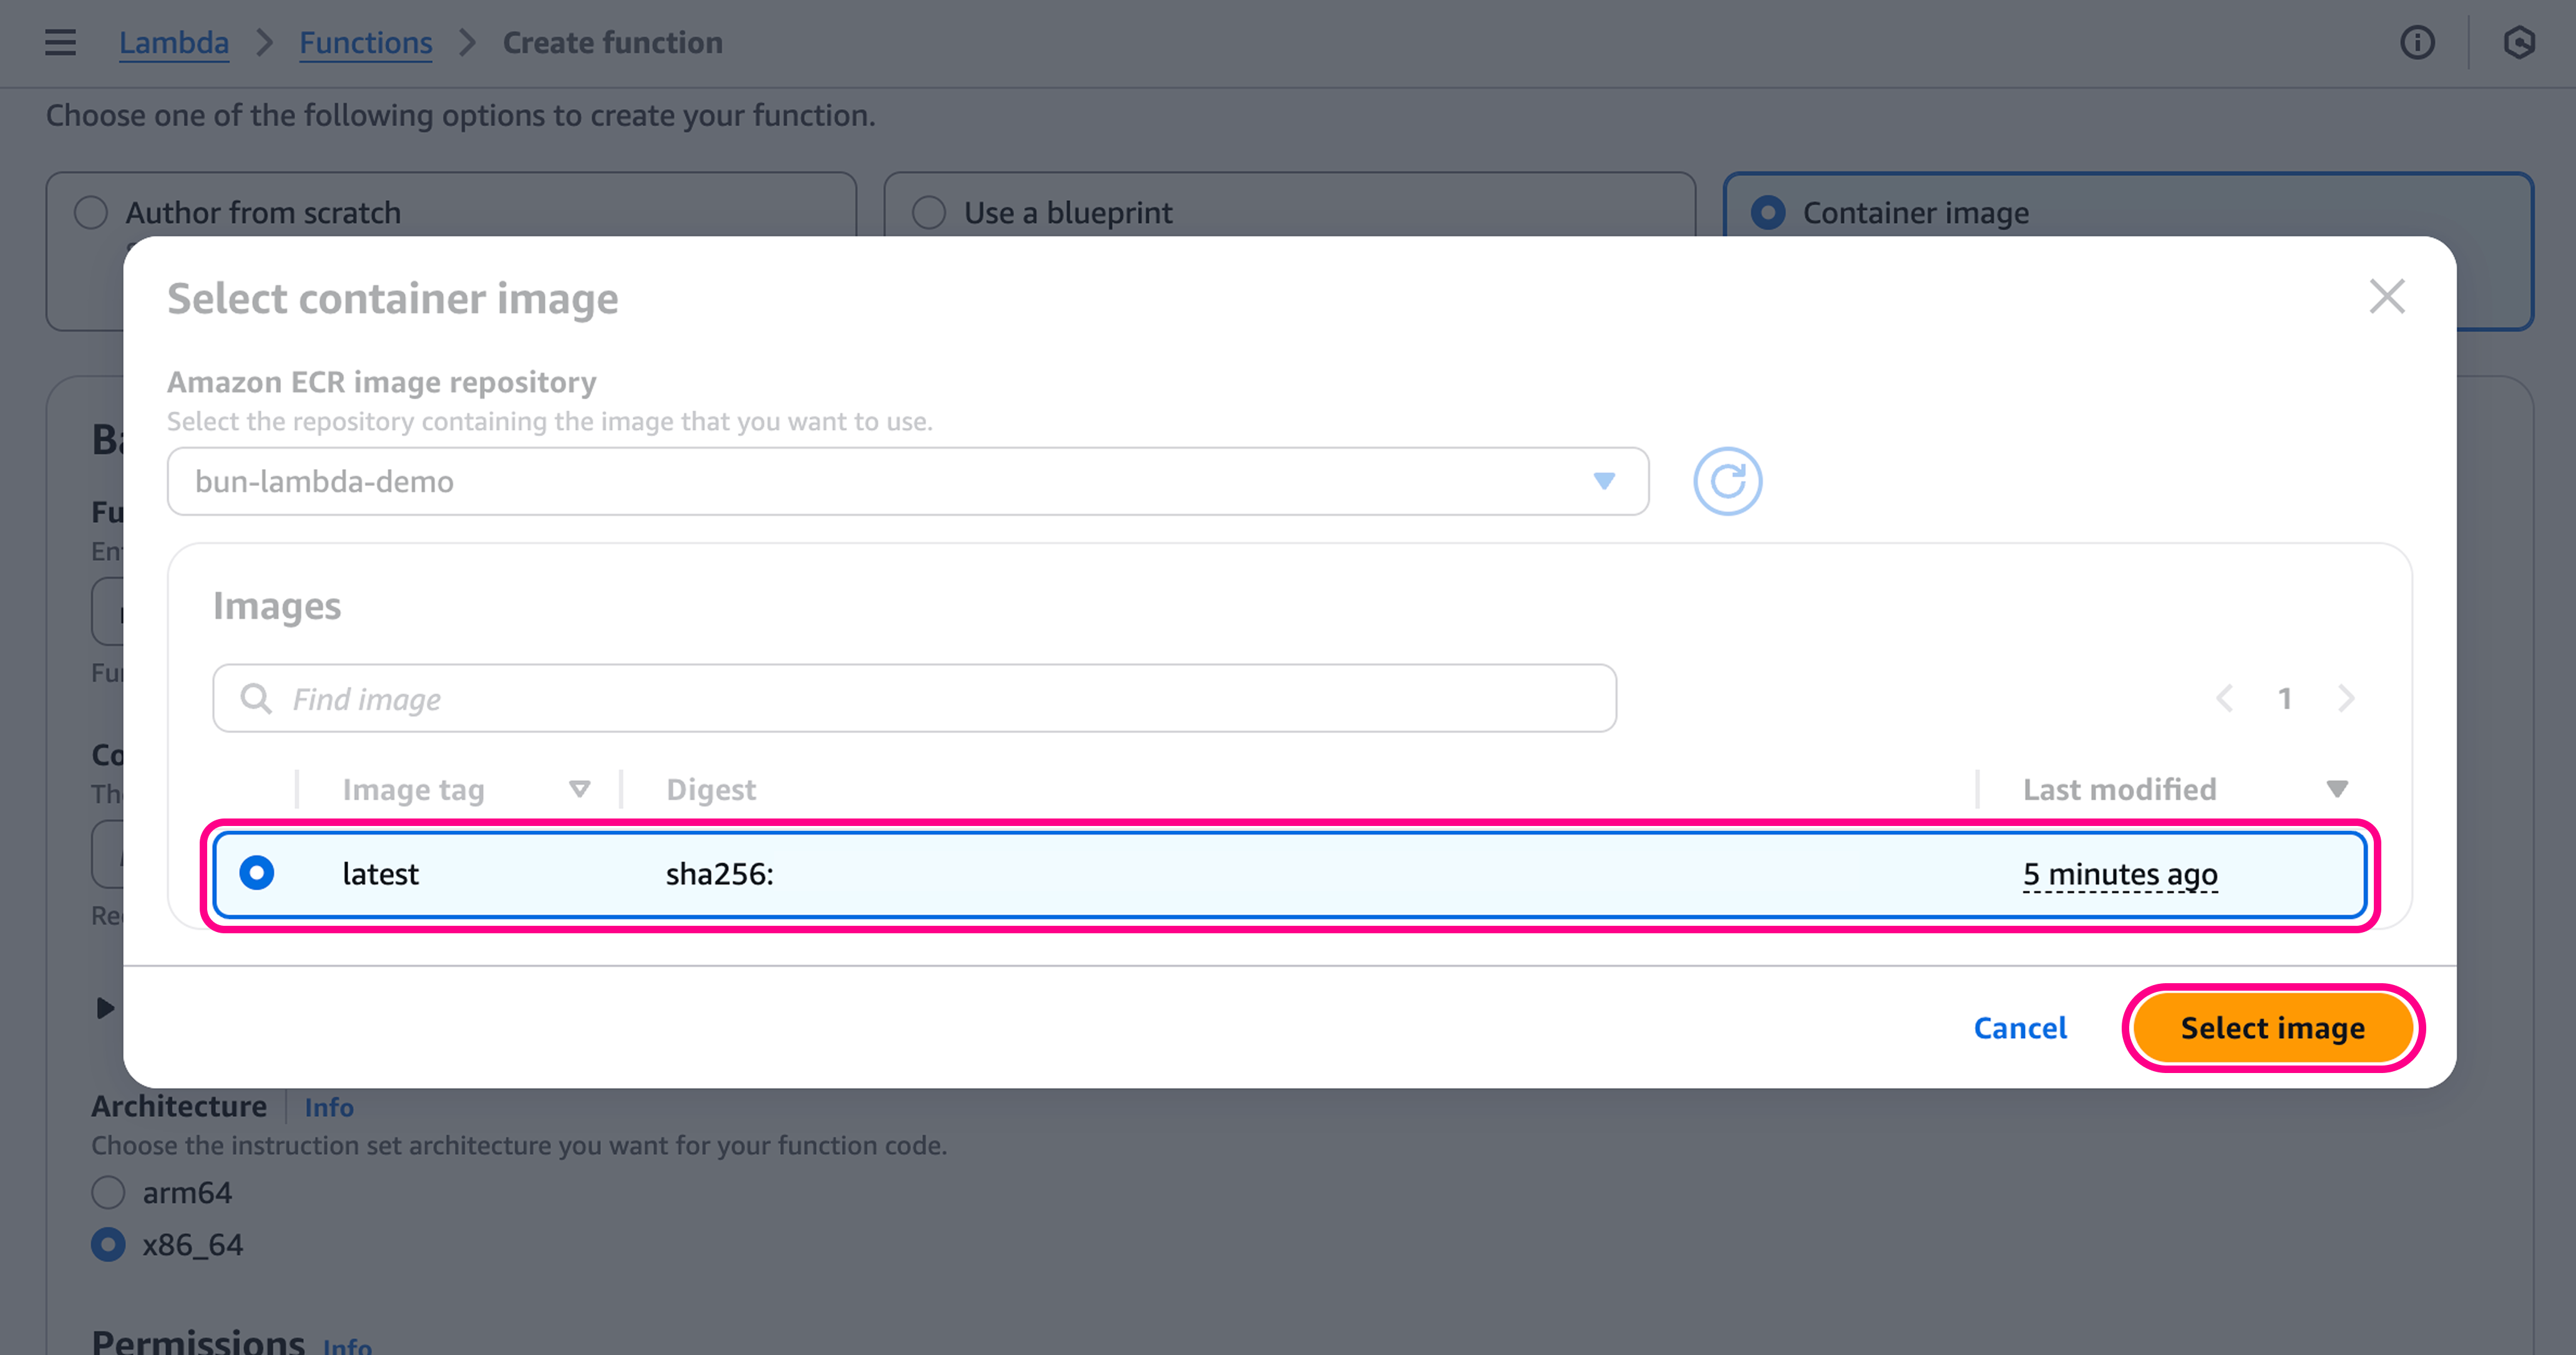
-
Configure the function
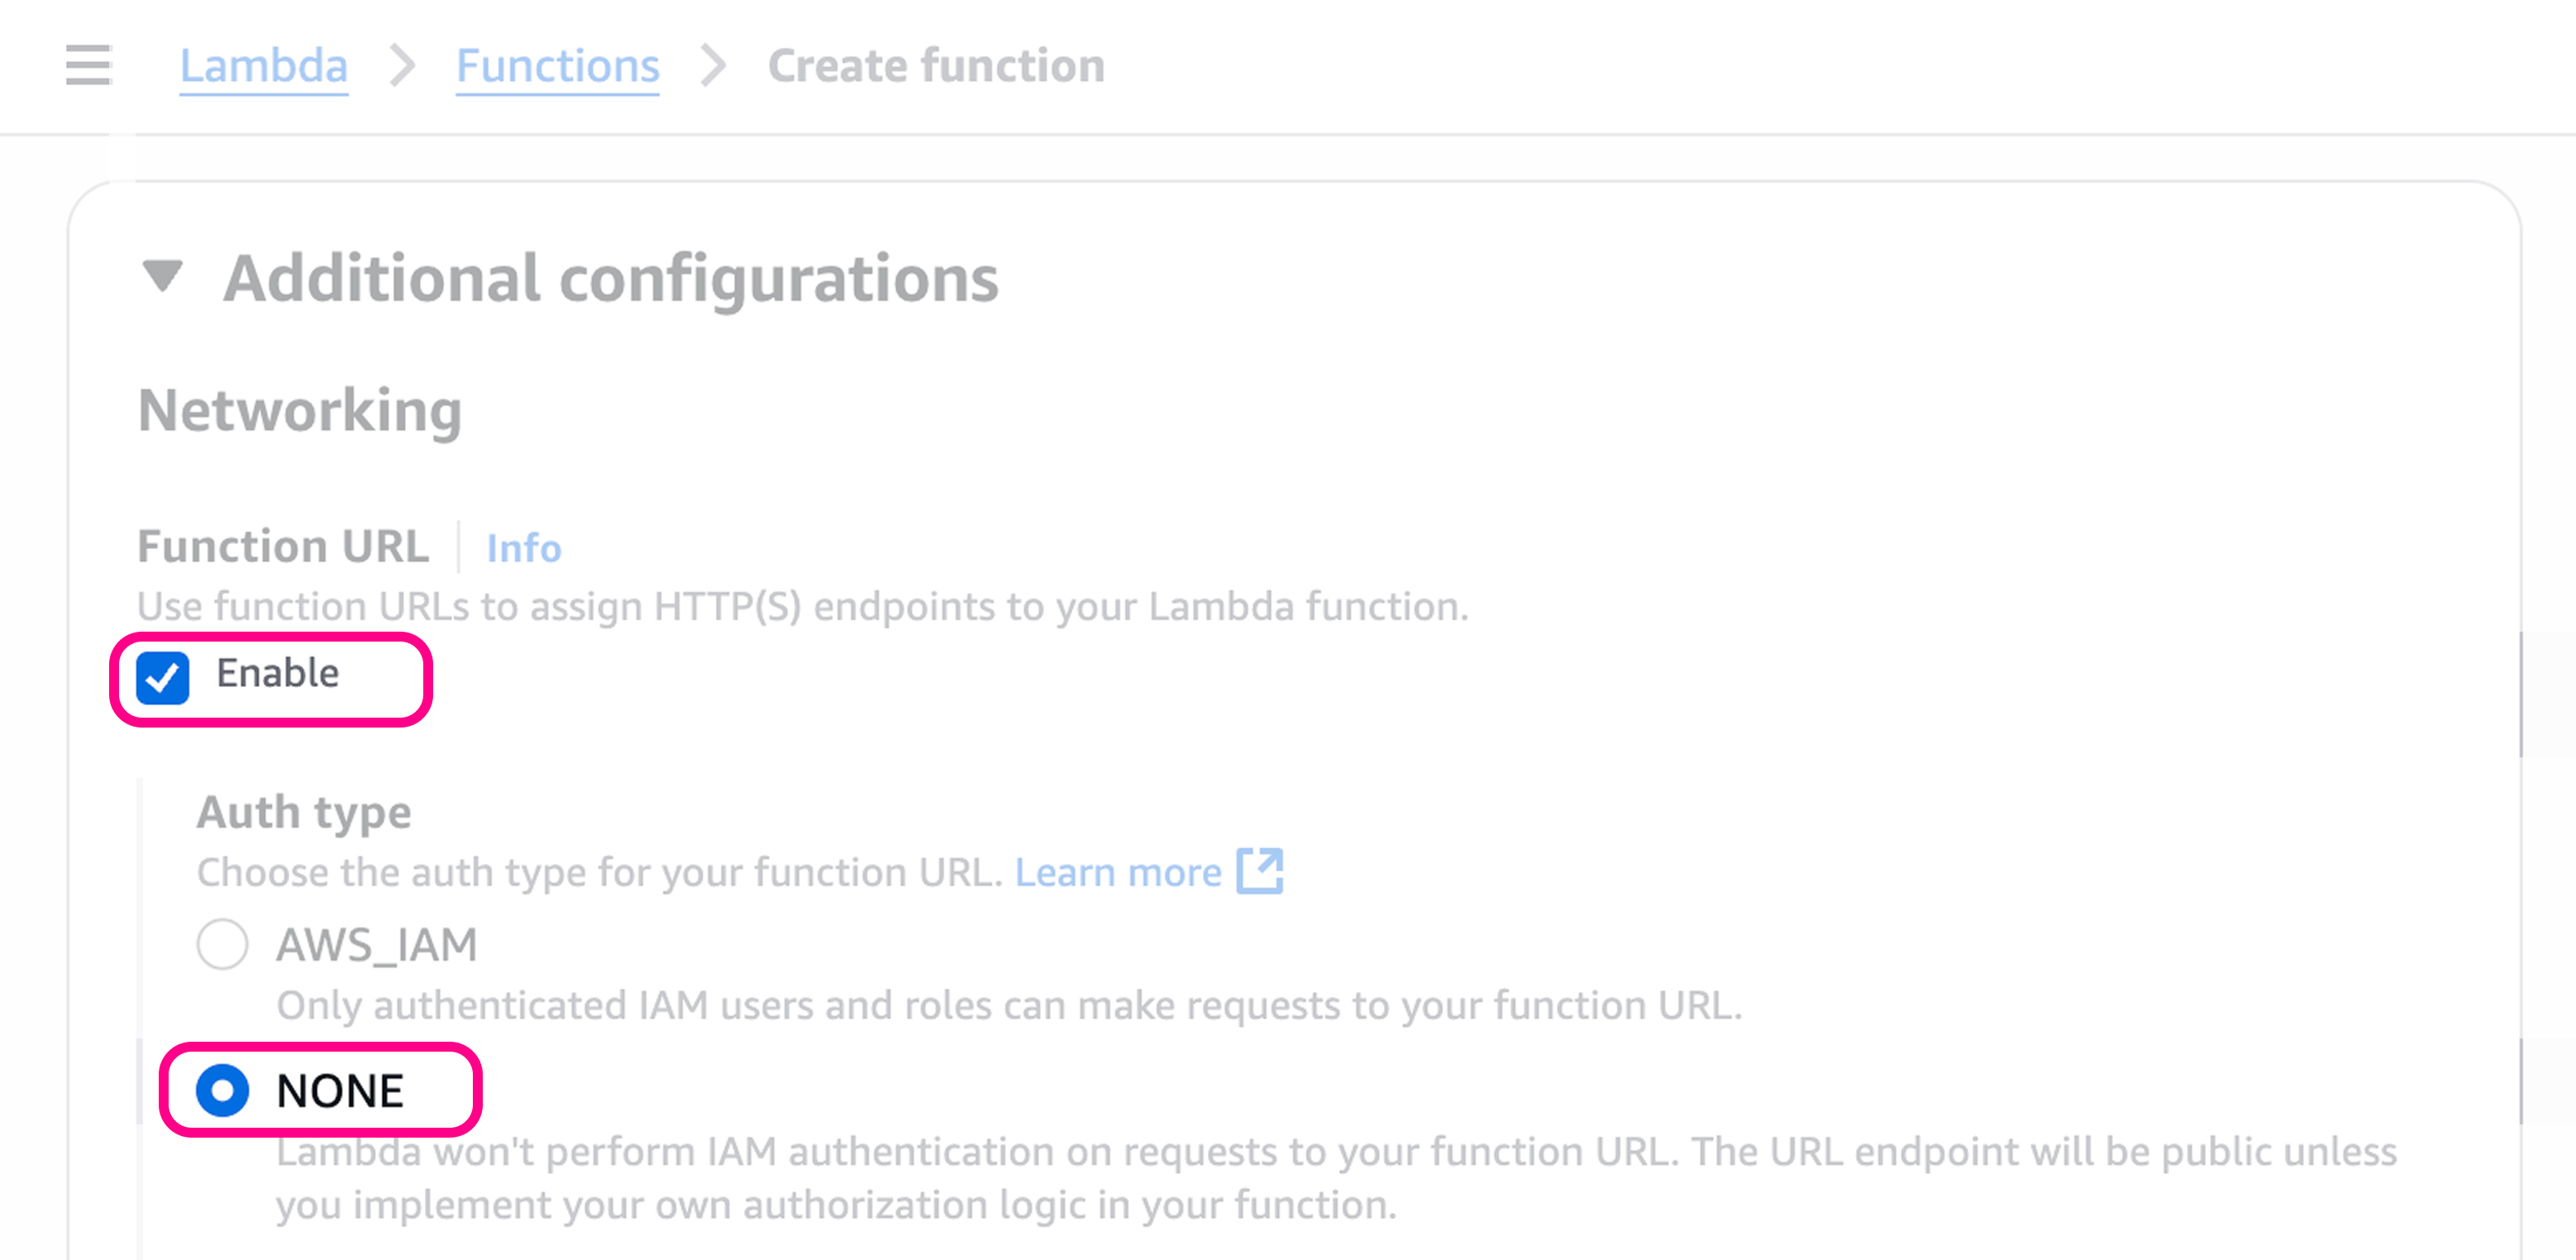
To get a public URL for the function, go to Additional configurations > Networking > Function URL.
Set this to Enable, with Auth Type NONE.
-
Create the function
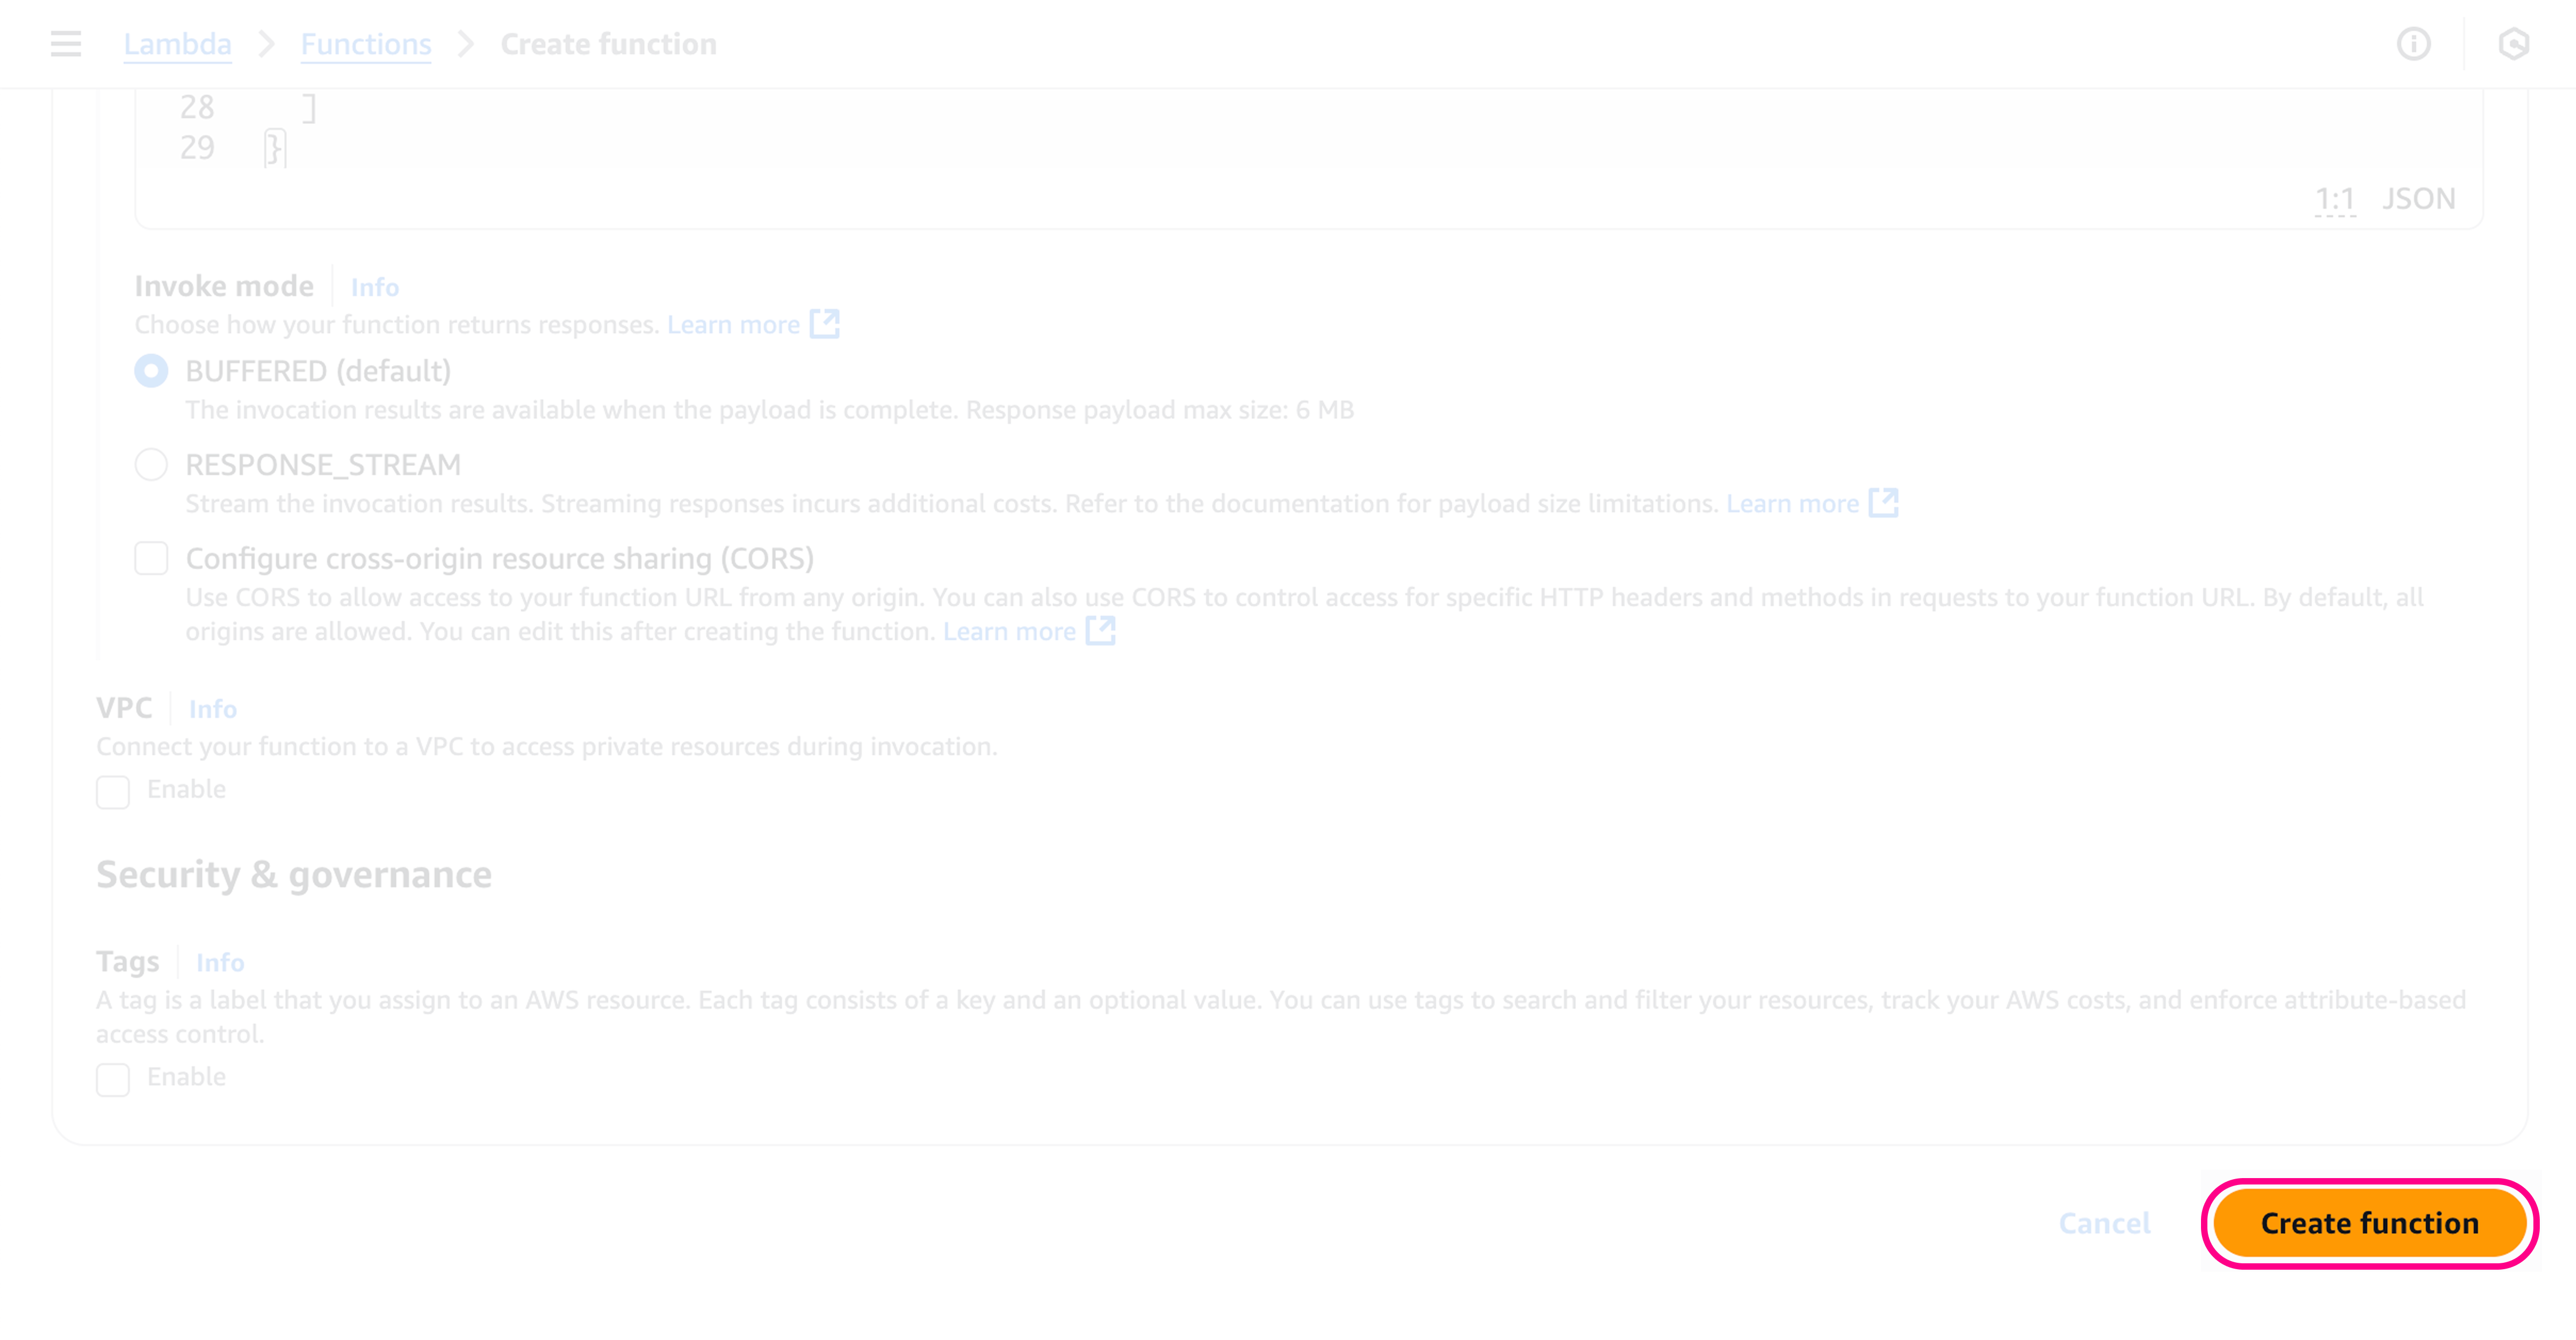
Click Create function at the bottom of the page.
-
Get the function URL
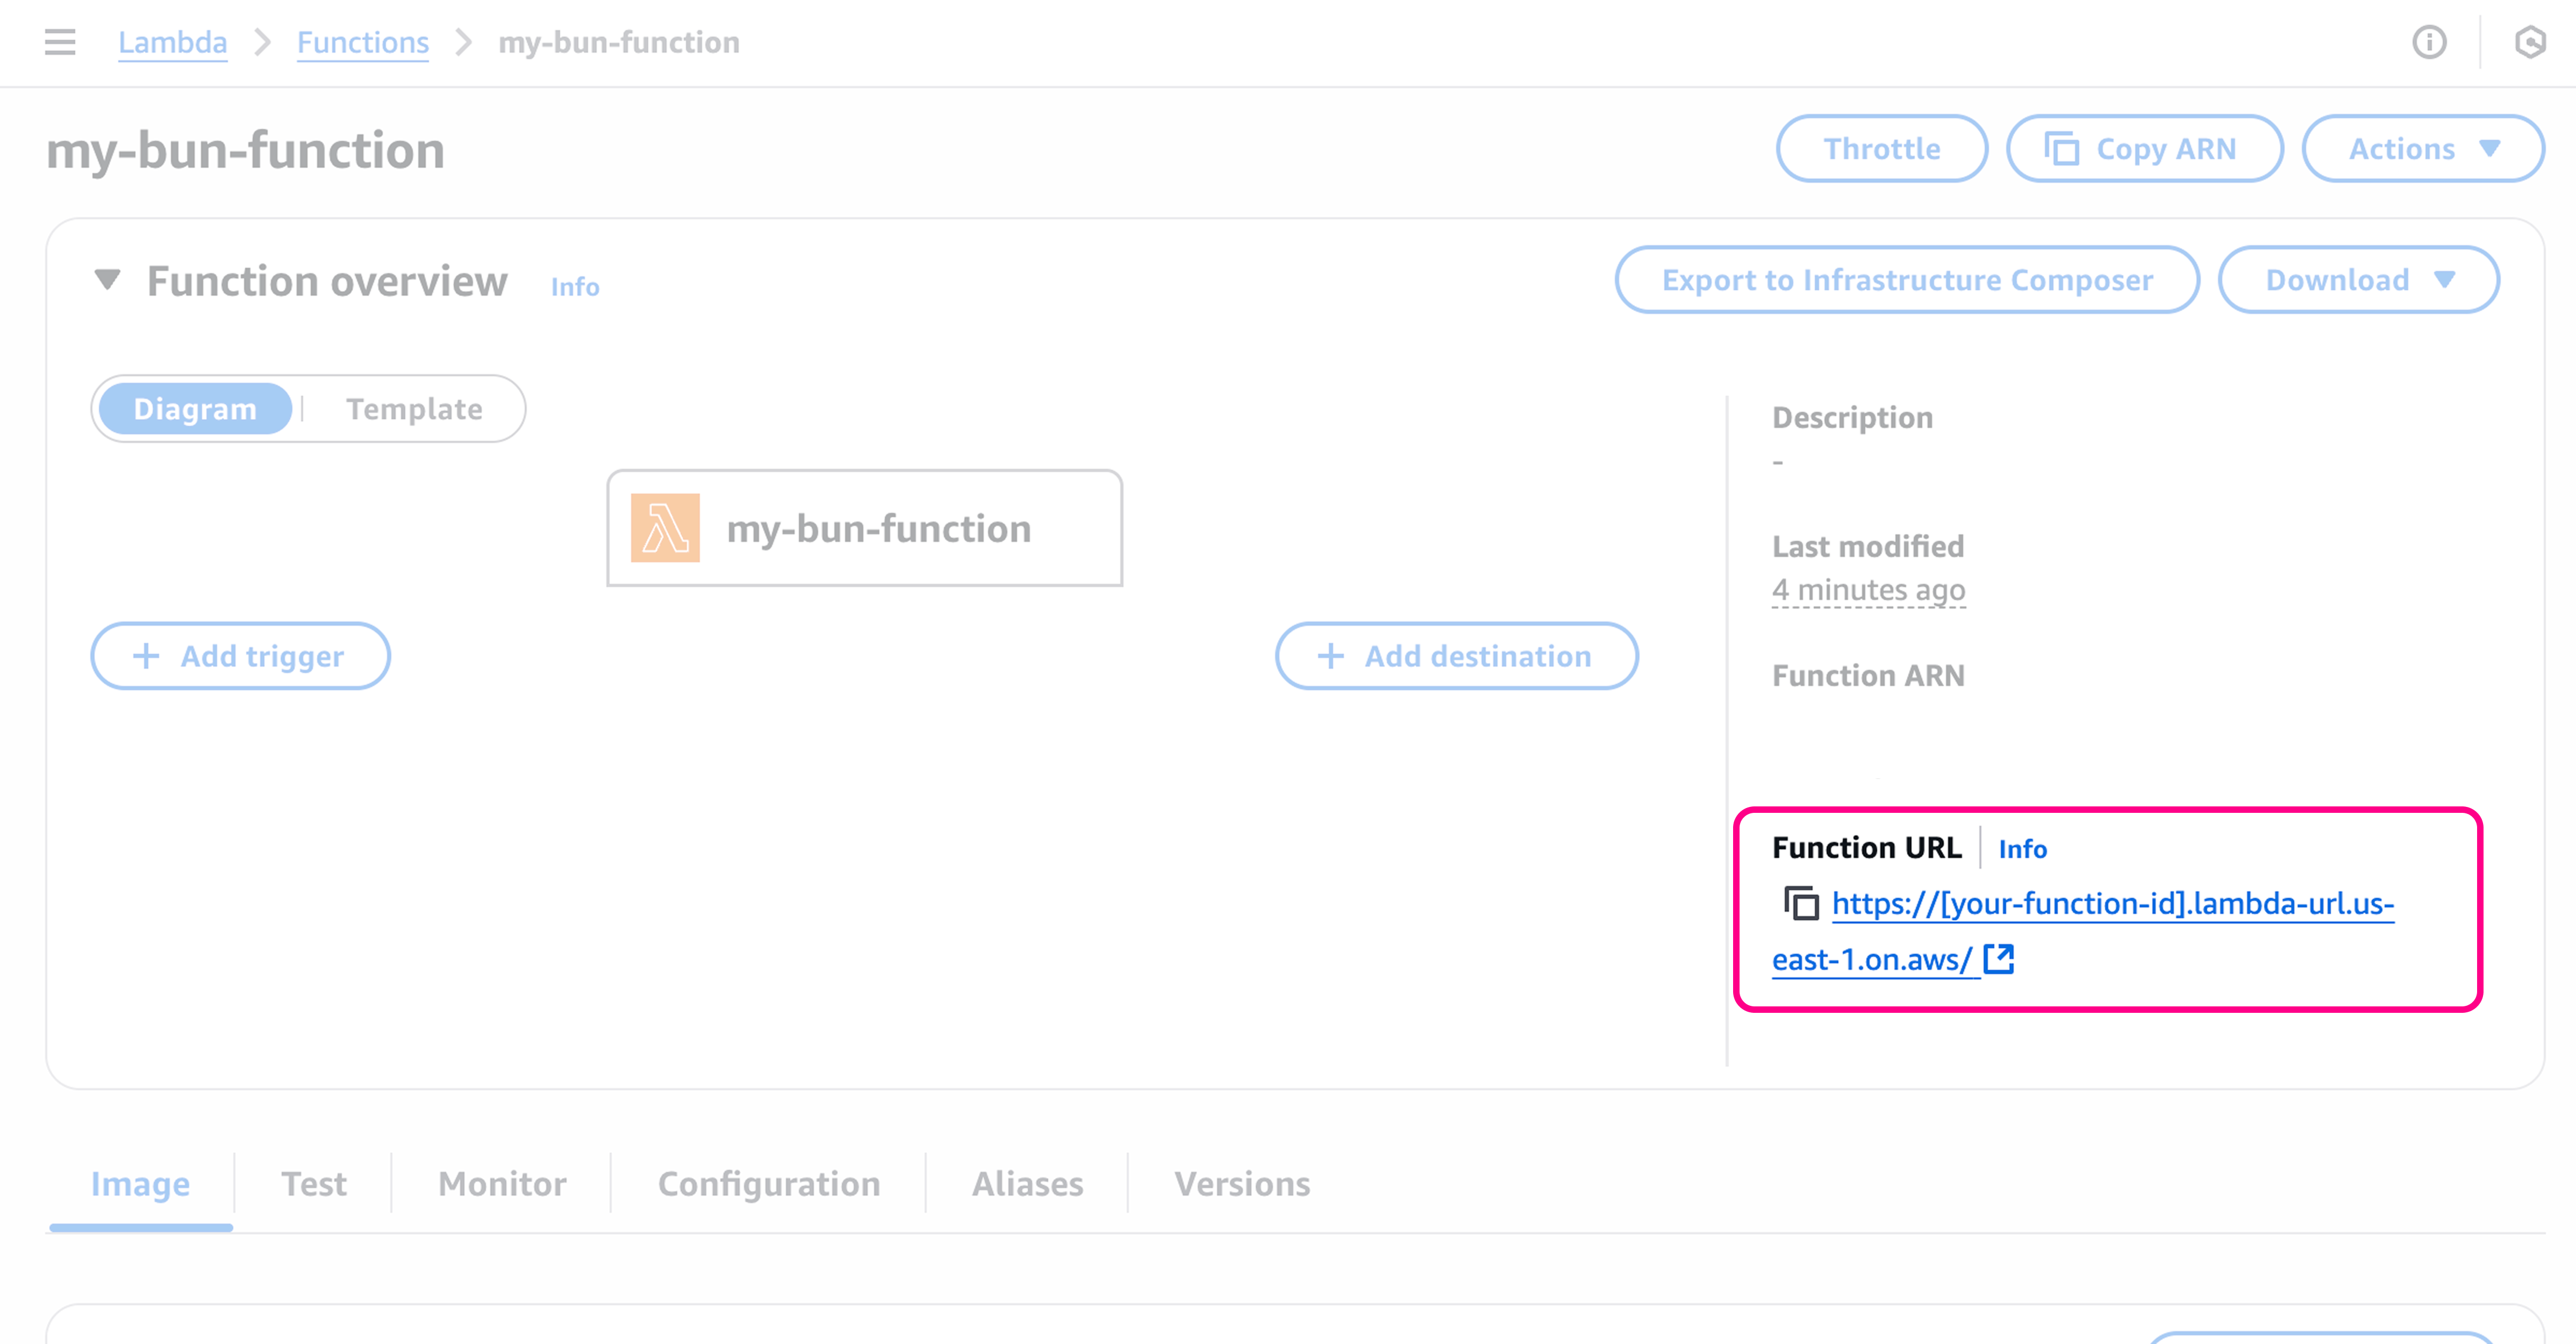
Once the function is created, you're redirected to its page. The function URL is in the "Function URL" section.
-
Test the function
Your app is now live. To test the function, either go to the Test tab or call the function URL directly.
curl -X GET https://[your-function-id].lambda-url.us-east-1.on.aws/Hello from Bun on Lambda!